
Data Protection Risk
DigiTorc works with organisations to implement cost effective and streamlined data handling measures. Successful data privacy transformation requires strong governance and leadership.
Organisations that process and hold personal data in their care are required to publish particular information and have the following policy and procedure documentation in place:
- Data Protection Policy.
- Data Privacy Notice, listing the purposes and legal bases that the organisation relies upon to collect personal data.
- Data Subject Rights Request Procedure.
- Data Breach Handling Procedure.
- Data Retention Policy.
In addition, organisations are obliged to undertake the following activities at various times and revisit later if necessary:
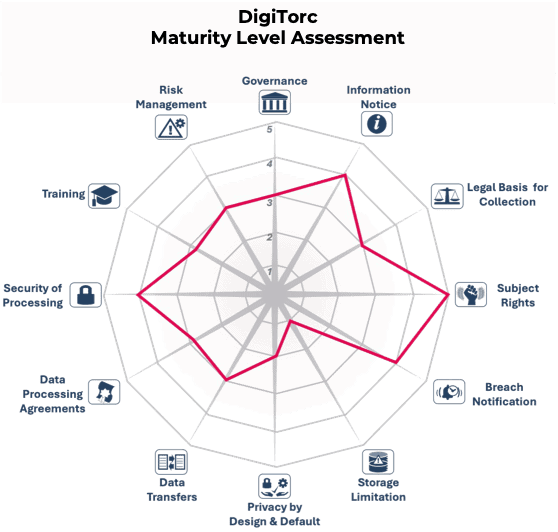
- Carry out a Maturity Level Assessment (MLA) to measure and highlight the gap between an organisation's current data protection posture and GDPR compliance levels to be bridged. The MLA is an important Risk Management exercise to undertake from time to time.
- Create and maintain a Record of Processing Activities (ROPA) when required by law.
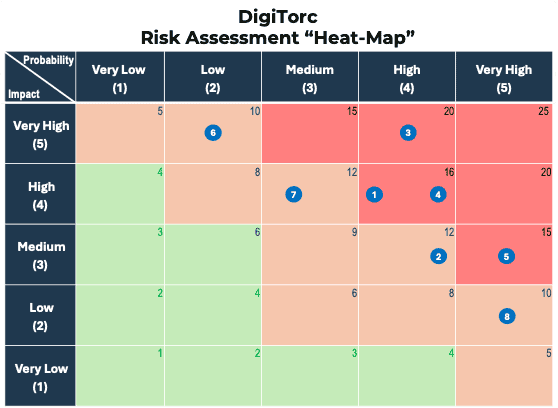
- Undertake a Data Protection Impact Assessments (DPIA) - a risk assessment - whenever a new processing activity could put the rights and freedoms of data subjects at risk.
- Carry out a Transfer Impact Assessment (TIA) when it is planned to transfer personal data to entities in jurisdictions without Adequacy Agreements in place with the EU Commission.
- Undertake a Legitimate Interest Assessment (LIA) when the organisation plans to rely on the legal basis "Legitimate Interest" to process personal data.
Our objective is to help organisations meet legal obligations without over-complicating matters. GDPR compliance is more than a mere tick-box exercise, the trustworthiness it imparts will enhance your brand; that's a key differentiator to help grow your business!
Our objective is to get your organisation compliant while not over complicating matters. GDPR can be a strategic differentiator helping businesses to grow, not just another compliance matter. Besides putting in place the various technology solutions, strategies, policies and plans required to meet EU GDPR requirements, we also offer an outsourced Data Protection Officer service and carry out any internal training or DPIAs that may be necessary.
AI Risk
Developers, manufacturers, importers, resellers and deployers of potentially High-Risk AI systems classified under the AI Act will be required to commission one or more of the following deliverables at various points throughout their AI Model Lifecycles.
- Convention 108: What and who?
- European Data Protection and Data Privacy law
- Do I have to do a Data Protection Impact Assessment?
- CCTV and Data Privacy: What’s the story?
- PECR: an Introduction
- Four key points to include in contracts between Data Controllers and Data Processors
- GDPR Data Retention: Adequate, relevant and not excessive
- Consent: one of six lawful bases to process personal data, in GDPR
- GDPR and Charities in Ireland
- Google Analytics and GDPR